Advisory Council - Veritas Institute
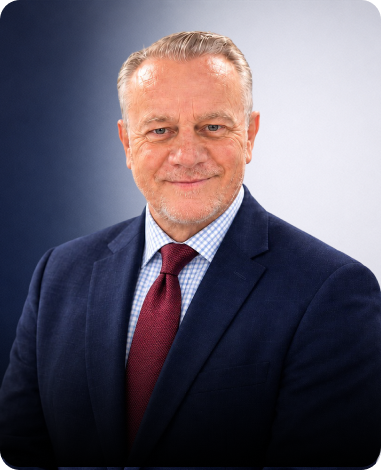
Andrew Robson, CISA, is a senior cybersecurity and technology executive whose career spans automotive manufacturing, financial services and military telecommunications. As Chief Information Security Officer at Bentley Motors, he leads and shapes cybersecurity strategy for a global automotive manufacturer, with responsibility for protecting critical systems, managing technology risk and sustaining trust in the business. He joins Veritas Institute’s Advisory Council and Subject Matter Expert, bringing extensive operational experience and an executive perspective on the relationship between security, organizational resilience and commercial performance.
At Bentley Motors, Andrew’s workplaces cybersecurity within the wider responsibilities of enterprise leadership. His focus encompasses the protection of systems essential to the organization, alongside the confidence of customers and the integrity of the brand. He connects security priorities with business objectives, helping establish the conditions in which innovation and sustainable growth can proceed with appropriate protection. This perspective gives his leadership a clear commercial relevance: security decisions must reflect what the organization needs to achieve and what it must be able to rely upon.
Andrew’s technical foundations were established in telecommunications with the Royal Air Force, where he gained experience in telecommunications and network systems. That grounding provided the basis for his subsequent career in information technology and security. It also gives depth to his executive perspective, connecting an understanding of the infrastructure on which organizations depend on the wider consequences of its disruption. His progression into senior leadership has developed from direct exposure to the systems and operational disciplines that effective security requires.
His career in financial services included Unix security at Lloyds TSB, where he supported secure infrastructure and operations within a major financial institution. This work developed his experience of platform protection in an environment where the reliability of underlying technology is essential to service delivery. It forms part of the practical foundation behind his broader expertise in security infrastructure and access management, areas in which clear controls and consistent operational practice support an organization’s ability to manage technology risk.
At Barclays, Andrew worked in global Unix security, delivering security across an international technology environment and strengthening platform security and operational stability. The global scope of this experience broadened his perspective on the application of security practices across complex organizations. It also added an international dimension to a career already grounded in the relationship between dependable infrastructure and effective business operations. This experience remains relevant to his understanding of how strategic security objectives translate into the protection of interconnected systems.
Andrew subsequently worked in security operations and security infrastructure at The Co-operative Bank. His focus included operational security, threat management and the development of resilient infrastructure within financial services. These responsibilities extended his experience beyond individual platforms into the operational demands of maintaining an effective security capability. Together, his banking roles established a substantial foundation for his later executive responsibilities, combining technical knowledge with an appreciation of the governance, continuity and customer confidence requirements of a complex enterprise.
Across these roles, Andrew has developed expertise in cybersecurity strategy and operations, technology risk and governance, security infrastructure, and access management. His professional scope also includes regulatory compliance, data protection, operational resilience and business continuity. These disciplines inform a connected view of enterprise security: the effectiveness of a technical safeguard must be understood alongside the risk it addresses, the operational dependency it protects and the governance arrangements that sustain it. His Certified Information Systems Auditor (CISA) credential complements this background and his focus on risk and controls.
Leadership and stakeholder engagement are central to Andrew’s professional approach. He links security to business priorities and emphasizes its contribution to customer trust, risk reduction and the capacity for sustainable growth. His combination of operational grounding and executive responsibility gives him a practical basis for discussing security with audiences whose priorities and technical knowledge differ. For senior leaders, this perspective helps place cybersecurity within decisions about organizational performance; for practitioners, it connects daily security activity with the outcomes that matter to the enterprise.
At Veritas Institute, Andrew will contribute this breadth of experience to its global advisory and subject matter expertise. His background is particularly relevant to professional development in cybersecurity leadership, technology risk, governance and organizational resilience. He brings a practitioner’s understanding of the journey from technical responsibilities to executive accountability, offering valuable context for professionals preparing to assume broader leadership roles. His contribution will help inform education that connects the principles of security management with the practical realities of protecting systems and maintaining business confidence.
Andrew’s experience across financial services and automotive manufacturing also adds a useful comparative perspective to Veritas Institute’s work. These sectors provide different settings in which to examine the relationship between technology, operational reliability and trust. His background offers a foundation for exploring how security priorities are shaped by an organization’s purpose and dependencies, and how leaders can apply their judgement across varied operating environments. For an institution serving a global professional audience, that breadth supports learning that is both strategically relevant and grounded in practical experience.
Andrew’s professional outlook is captured in his belief that “Security works best when it protects people, enables business and builds trust.” This principle provides a consistent thread through his career, from telecommunications and platform security to enterprise cybersecurity leadership. In joining Veritas Institute, he brings that perspective to the development of security professionals who must understand the technical demands of their field while exercising the judgement and business awareness expected of senior leadership.